Overview: The Cross-Chain Interoperability Trilemma and Generalized Messaging
The proliferation of heterogeneous Layer 1 blockchains, optimistic rollups, zero-knowledge execution layers, and application-specific appchains has permanently fractured state and liquidity across Web3. In the early era of decentralized finance, interoperability was dominated by isolated, pairwise token bridges. These legacy mechanisms relied on fragmented liquidity pools or bilateral lock-and-mint architectures, creating isolated multi-sig honeypots that suffered catastrophic smart contract exploits and severe capital inefficiency.
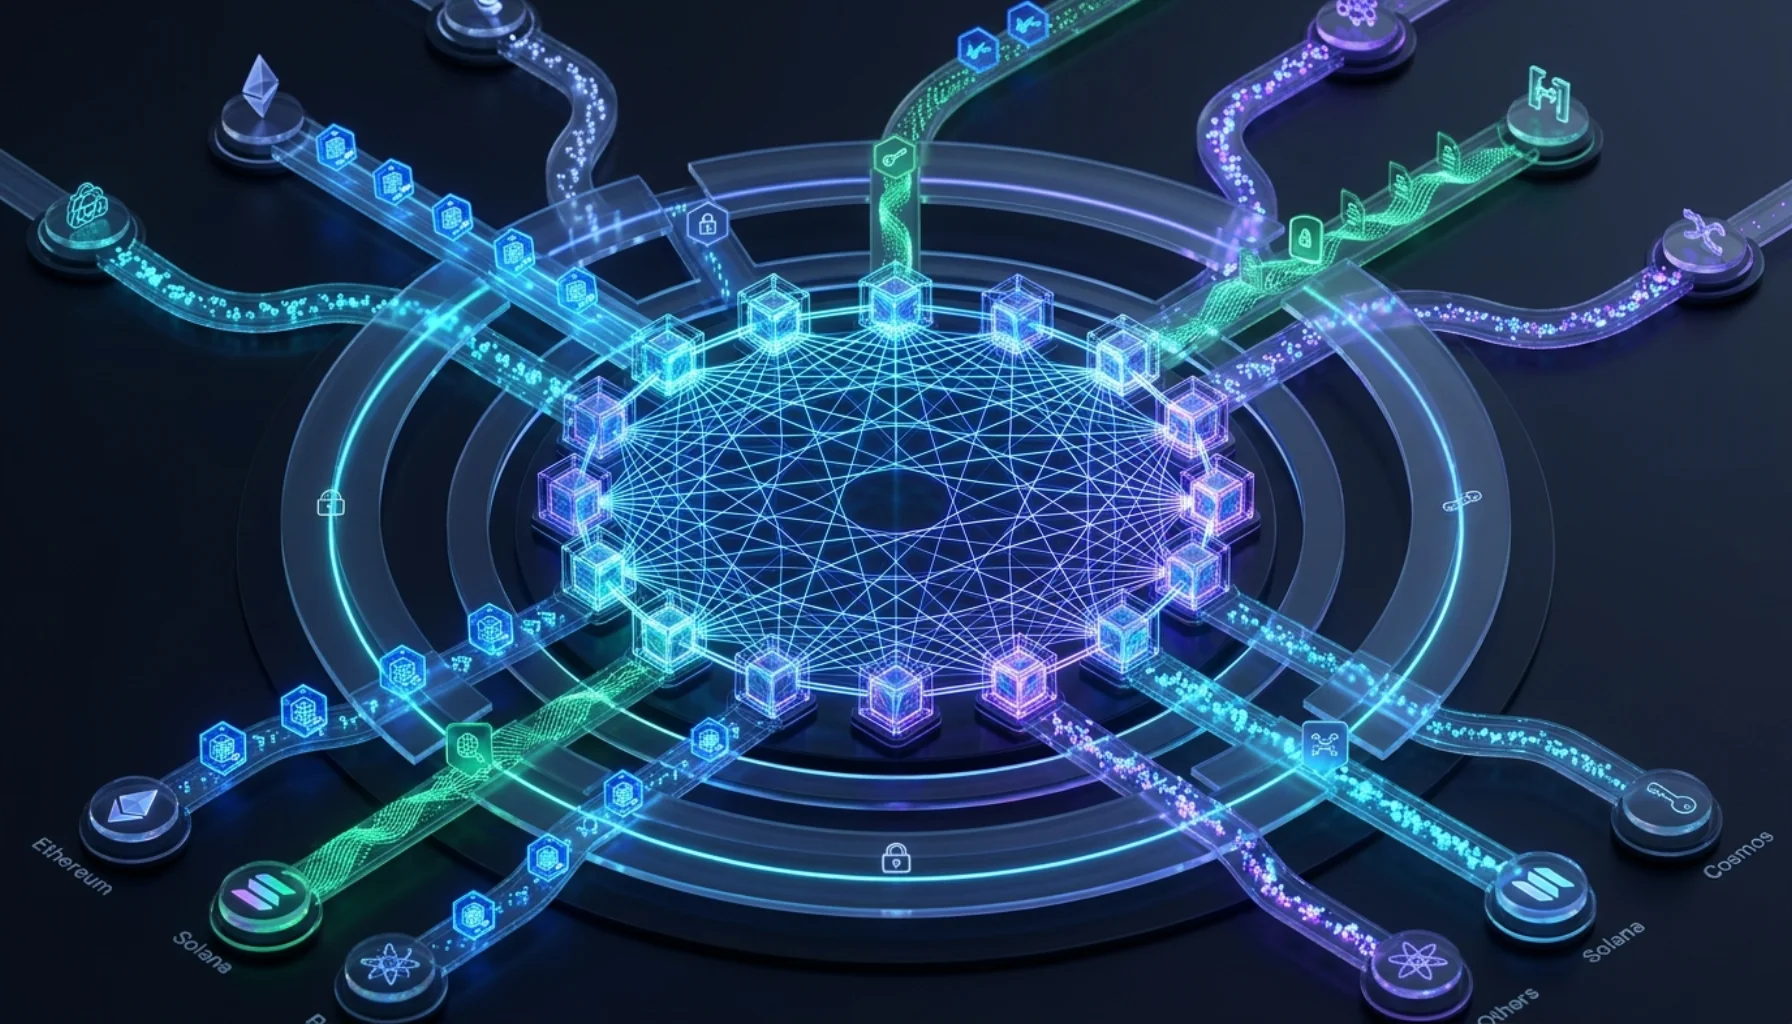
Wormhole emerged to resolve this structural fragmentation by fundamentally redefining cross-chain communication. Rather than operating as a specialized asset bridge, Wormhole is architected as a generalized, trust-minimized message-passing protocol. Wormhole provides a universal interoperability substrate that enables independent blockchains: spanning Ethereum Virtual Machine (EVM) chains, Solana (SVM), Move-based execution environments (such as Sui and Aptos), and Cosmos appchains via the Cosmos Inter-Blockchain Communication (IBC) standard: to verify arbitrary state transitions and exchange verifiable data payloads.
At its architectural foundation, Wormhole decouples state observation and attestation from execution and relaying. By routing cross-chain communications through a decentralized network of 19 independent institutional validators known as the Guardian Network, Wormhole compiles multi-chain state events into cryptographically signed verifiable packets called Verified Action Approvals (VAAs). With cumulative cross-chain transfer volume exceeding $40 billion and hundreds of integrated decentralized applications, Wormhole serves as foundational routing infrastructure for decentralized finance, governance, oracle data distribution, and native asset transfers.
The Wormhole Core Layer: Anatomy of an Interoperable Message
The Wormhole messaging lifecycle is partitioned into distinct layers: the on-chain Core Contracts, the off-chain Guardian Network, the off-chain Relayer infrastructure, and target chain consumer applications.
1. Sequence of Cross-Chain Interaction
The canonical path of a cross-chain transaction through Wormhole proceeds through four sequential stages:
- Source Chain Emission: A decentralized application on a source blockchain invokes the Wormhole Core Contract, passing an arbitrary byte payload and specifying a required finality consistency level.
- Guardian Observation: Independent Guardian nodes run full archive nodes for all connected blockchains, observing the emitted event log after the requested block confirmation threshold has elapsed.
- Off-Chain Gossip and Attestation: Guardians validate the transaction against their local full node state, generate an ECDSA signature over the message hash, and broadcast the attestation over a peer-to-peer gossip network.
- VAA Assembly and Relaying: Once a supermajority of Guardians signs the message, the individual signatures are assembled into a single Verified Action Approval (VAA) packet and dispatched by off-chain relayers to the destination blockchain for execution.
2. The Core Contract Interface and Parameters
Every blockchain connected to Wormhole deploys an instance of the Wormhole Core Contract. When an application initiates a cross-chain message, it calls the protocol's primary entry point: publishMessage. This function requires three fundamental parameters:
- Payload (bytes): The arbitrary binary data payload to be conveyed to the target blockchain. This may encode token transfer parameters, remote contract invocation instructions, or governance votes.
- Nonce (uint32): A client-defined numerical identifier used to coordinate message batching or sequence tracking across asynchronous transactions.
- Consistency Level (uint8): The security threshold defining how many block confirmations the Guardian Network must observe before attesting to the message. On Ethereum, consistency levels can enforce either immediate unfinalized blocks, safe head blocks, or finalized epochs (two full Casper FFG epochs, approximately 64 to 96 slots). On Solana, consistency levels differentiate between 'processed', 'confirmed', and 'finalized' commitments. This explicit parameter guarantees that temporary blockchain reorgs on the source chain cannot produce false cross-chain attestations.
3. Emitter Identity and Replay Protection
To prevent spoofing and unauthorized cross-chain state modification, the Core Contract automatically wraps the user payload into a standardized message envelope. The Core Contract records:
- Emitter Chain ID: A universal 16-bit unsigned integer deterministically assigned to each blockchain within the Wormhole ecosystem (e.g. Ethereum is Chain 2, Solana is Chain 1, BNB Chain is Chain 4).
- Emitter Address: The universal 32-byte identifier (left-padded with zeros for 20-byte EVM addresses) of the invoking smart contract on the source chain. Because the Core Contract stamps its caller as the emitter, target contracts can enforce cryptographic access controls based on known, authorized emitter contracts.
- Sequence Number: A monotonically increasing 64-bit integer maintained individually for each emitter address. The sequence number guarantees total ordering of messages originating from a specific contract and provides mathematical replay protection on target blockchains.
The Guardian Network: P2P Gossip Consensus and Multi-Signature Attestation
While the Wormhole Core Contracts handle on-chain emission and verification, the cryptographic trust model rests entirely upon the Guardian Network.
1. Composition and Validator Topology
The Guardian Network is composed of 19 independent institutional validators and premier infrastructure engineering firms. The validator set includes established entities such as Jump Crypto, Everstake, Figment, Chorus One, Staked, xLabs, and P2P Validator. These operators are selected based on high infrastructure availability, institutional security standards, multi-cloud hardware redundancy, and extensive experience running bare-metal validator operations across dozens of disparate blockchain protocols.
Each Guardian node runs a specialized software client known as guardiand. Alongside the daemon, each Guardian maintains dedicated, independent full nodes or archive nodes for every single blockchain connected to the Wormhole protocol. This direct node requirement eliminates reliance on centralized third-party RPC providers (such as Infura or Alchemy), ensuring that Guardians independently verify block headers, state trie roots, and event logs directly from peer-to-peer block gossip.
2. P2P Gossip via Libp2p and Spy Nodes
The Guardian nodes communicate over a private, high-performance peer-to-peer gossip network built on the libp2p framework. When an individual Guardian observes that a publishMessage event on a connected chain has met its specified consistency level, the node generates a SHA-256 hash of the standardized message body.
The Guardian signs this hash using its dedicated Secp256k1 ECDSA private key. The node then broadcasts an observation message containing the signature across the libp2p gossip mesh. Observers and infrastructure providers can deploy read-only Spy nodes into this gossip network to monitor active cross-chain traffic in real time without possessing signing authority.
3. The Two-Thirds Supermajority Invariant
Wormhole enforces a strict Byzantine fault-tolerant quorum threshold. To assemble a canonically valid VAA, a message must collect signatures from more than two-thirds of the active Guardian set plus one:
Threshold = \lfloor \frac{2N}{3} \rfloor + 1
With an active set of $N = 19$ Guardians, exactly 13 signatures are required to validate any cross-chain action. This 13 of 19 threshold guarantees that:
- The protocol can tolerate up to 6 completely unresponsive or offline Guardian nodes without halting cross-chain liveness.
- An adversary would need to corrupt or compromise at least 13 independent, institutional validators simultaneously to forge an illegitimate cross-chain message.
- A colluding minority of up to 6 malicious Guardians cannot censor transactions or produce unauthorized state modifications.
4. Attestation Without Execution
A crucial design invariant of the Guardian Network is the strict separation between attestation and execution. Guardians never submit transactions to destination blockchains, never hold gas tokens on destination networks, and never manage destination private keys. Their sole cryptographic responsibility is signing valid state observations. The task of transporting and submitting signed VAAs to destination contracts is delegated entirely to the decentralized Relayer layer.
Anatomy of a Verified Action Approval (VAA)
The Verified Action Approval (VAA) is the fundamental atomic data packet of the Wormhole protocol. It is an immutable, self-contained cryptographic payload that can be independently verified by any smart contract on any blockchain without requiring external state queries.
1. Binary Packet Wire Format
A VAA is serialized into an optimized binary format designed for low gas consumption during on-chain cryptographic parsing. The VAA layout consists of two primary segments: the Header and the Body.
- VAA Header:
version (uint8):Protocol version identifier (currently 1).guardian_set_index (uint32):The sequential index of the Guardian validator set that signed the message, allowing seamless validator set rotations.signatures_len (uint8):The total count of Guardian signatures attached (minimum 13).signatures (array):A contiguous array of 66-byte signature blocks. Each block contains:guardian_index (uint8):The positional index of the signing Guardian within the active set.r (bytes32):The r-component of the ECDSA signature.s (bytes32):The s-component of the ECDSA signature.v (uint8):The recovery identifier (0 or 1, normalized to 27/28 for EVM compatibility).
- VAA Body:
timestamp (uint32):Unix epoch timestamp recorded when the message was published on the source chain.nonce (uint32):Client-specified nonce for batching or tracking.emitter_chain (uint16):Universal Wormhole Chain ID of the origin blockchain.emitter_address (bytes32):Origin smart contract address formatted as a universal 32-byte array.sequence (uint64):Monotonically increasing sequence number assigned by the source Core Contract.consistency_level (uint8):Block confirmation threshold satisfied on the source chain.payload (bytes):The raw arbitrary application byte payload.
2. On-Chain Verification Algorithm
When a VAA is delivered to a destination blockchain Core Contract, the contract executes the parseAndVerifyVM verification routine:
- Double-Hash Generation: The contract extracts the VAA Body bytes and computes a double SHA-256 hash:
hash = keccak256(abi.encodePacked(sha256(sha256(vaaBody))))(or native hashing tailored to the target virtual machine). - Guardian Set Validation: The contract checks that
guardian_set_indexmatches either the currently active Guardian set or a recent set within its valid grace expiration window. - Signature Loop and Elliptic Curve Recovery: The contract loops through the attached signatures, verifying that the number of signatures meets or exceeds the quorum threshold (13). For each signature, it executes the elliptic curve recovery primitive (e.g.
ecrecoveron EVM, or Ed25519/Secp256k1 precompiles on SVM/CosmWasm). - Ordering and Duplicate Checking: The verification algorithm strictly asserts that the
guardian_indexvalues in the array are strictly ascending (e.g. index 2 followed by index 5, then index 8). This check mathematically guarantees in O(N) operations that no individual Guardian signature is counted multiple times.
Once all cryptographic assertions pass, the VAA is verified. The destination smart contract can safely parse the payload and execute state mutations with mathematical finality.
Relayer Architectures: Specialized vs. Automatic Delivery
Because the Guardian Network only produces signed VAA blobs off-chain, an intermediary must deliver the VAA to the destination blockchain and pay the required transaction gas fees. This transport layer is handled by Relayers.
1. Specialized Relayers
In a specialized relayer architecture, the decentralized application developers run their own off-chain daemons. The specialized relayer connects to Wormhole Spy nodes or public Guardian RPC APIs, filters for messages emitted by their specific contract address, and crafts custom destination transactions.
Specialized relaying is optimal for high-throughput or complex workflows where the application requires fine-grained control over execution ordering, transaction batching, gas pricing strategies, or multi-step DeFi interactions (such as automated swap-and-deposit workflows).
2. Standard Automatic Relayers
To relieve developers from the operational complexity of managing bare-metal relayer infrastructure and managing gas token balances across dozens of distinct blockchains, Wormhole introduced the Automatic Relayer Network.
Under the automatic relayer framework, the sender includes a fee payment directly on the source chain when calling the WormholeRelayer contract. The contract calculates the required destination execution cost using dynamic on-chain gas oracles. A decentralized network of third-party delivery providers monitors these requests, picks up the resulting VAAs, and guarantees delivery to the destination contract within a predefined gas limit. If execution on the destination chain fails due to contract logic errors, the relayer still receives compensation for gas spent, and the user receives a verifiable failure receipt.
Wormhole Gateway and Cosmos IBC Integration
Bridging into the Cosmos ecosystem has historically presented severe architectural friction. The Cosmos network consists of dozens of sovereign, independent appchains communicating via the Inter-Blockchain Communication (IBC) protocol. Deploying the full 19-node Wormhole Core Contract and verifying multi-signature VAAs on every individual Cosmos chain would consume prohibitive development effort and on-chain gas costs.
1. The Gateway Architecture
To unify liquidity between external ecosystems and the Interchain, the protocol launched Wormhole Gateway. Gateway is an application-specific blockchain built using the Cosmos SDK and secured by CometBFT consensus. Gateway functions as an architectural translation router:
- It maintains a direct connection to the Wormhole Guardian Network, deploying Core Contracts capable of verifying standard VAAs.
- It maintains native IBC connections with sovereign Cosmos appchains (such as Osmosis, Injective, Neutron, and Sei).
- When assets or messages flow from Ethereum or Solana toward Cosmos, Gateway verifies the incoming VAA once. It then wraps the payload into a standard ICS-20 IBC transfer packet and routes it permissionlessly to the target Cosmos appchain.
2. Liquidity Fungibility and ICS-20 Unification
A persistent flaw of multi-chain bridging was the proliferation of non-fungible wrapped asset variants (e.g. Wormhole ETH vs. Axelar ETH vs. Gravity ETH). Wormhole Gateway resolved this by enabling native IBC token translation. Assets entering Cosmos through Gateway can be mapped into standardized IBC denom hashes, preventing fragmented liquidity pools across decentralized exchanges in the Interchain.
Native Token Transfers (NTT): Eliminating Wrapped Token Fragmentation
The standard bridge design pattern for the past decade relied on canonical lock-and-mint wrapping. An original token was locked in a vault contract on Chain A, and an artificial wrapped derivative was minted on Chain B. If the vault on Chain A was ever exploited or frozen, the wrapped tokens on Chain B instantly lost their backing and collapsed to zero.
1. The NTT Protocol Model
Wormhole's Native Token Transfers (NTT) framework is an open-source, permissionless standard that allows token issuers to retain full sovereignty over their assets across multiple blockchains without relying on centralized bridge liquidity pools or canonical wrapped representations.
NTT supports two primary operational modes:
- Burn-and-Mint: On blockchains where the token contract grants minting permissions to the NTT manager contract, cross-chain transfers destroy native tokens on the source chain and mint authentic native tokens on the destination chain. The total circulating supply across all chains remains constant, and zero wrapped tokens are created.
- Lock-and-Mint (or Lock-and-Unlock): For tokens with fixed supplies deployed on chains where contracts cannot be modified (such as Ethereum L1), the NTT manager locks tokens in a secure custody vault on the origin chain while using burn-and-mint mechanics across all secondary L2s or alt-L1s.
2. Rate Limiting and Invariant Security
A critical innovation in NTT is modular risk management. Token issuers configure dynamic Rate Limiters directly within the on-chain NTT contracts. For example, an issuer can mandate that no more than $5 million worth of tokens can be minted or burned within any rolling 24-hour window. If an off-chain infrastructure compromise occurs, the rate limiter strictly caps potential loss, preventing an attacker from draining cross-chain liquidity before governance can intervene.
Furthermore, NTT is completely bridge-agnostic. While it natively utilizes Wormhole VAAs for attestation, the NTT architecture allows token issuers to configure multi-transceiver quorums, requiring attestations from Wormhole and secondary verification layers (such as Axelar or Chainlink CCIP) simultaneously before tokens are minted.
Wormhole Queries: Pull-Based Cross-Chain State Attestation
Traditional cross-chain interoperability operates on a "push" model: a user must execute an expensive on-chain transaction on the source blockchain to emit an event log before data can be relayed. For applications that simply need to verify state: such as checking account balances, reading price oracle records, or inspecting governance stakes: the push model imposes unacceptable latency and prohibitive gas costs.
1. Architecture of Cross-Chain Queries
Wormhole Queries introduces an on-demand "pull" model for cross-chain data access. Instead of submitting a transaction on the source chain, an application issues an off-chain REST or gRPC query to the Guardian Network specifying the exact contract address and storage slot or block header it wishes to inspect.
- Direct State Extraction: Guardian nodes query their local archive nodes, extracting the exact storage slot values or contract call outputs.
- Cryptographic Proof Generation: Guardians construct a cryptographic response envelope containing the requested data alongside an eth_call or account storage proof.
- Multi-Sig Attestation: Guardians sign the query result using their standard Secp256k1 keys.
- On-Chain Consumption: The application submits the signed query response directly to its destination contract. The destination contract verifies the Guardian signatures and instantly reads the verified foreign chain state.
Wormhole Queries achieves sub-second response times and reduces cross-chain data retrieval costs by more than 80%, enabling real-time cross-chain lending indexation, dynamic liquidation calculations, and unified multi-chain portfolio tracking.
Cryptoeconomic Security, The W Governance Token, and MultiGov
The governance and decentralization roadmap of Wormhole is anchored by its native governance token, W.
1. Token Supply and Allocation Architecture
The W token was instantiated with a total maximum supply of 10,000,000,000 W tokens across native SPL (Solana) and ERC-20 (Ethereum/EVM) formats. The initial distribution allocated capital across strategic ecosystem categories:
- Community and Launch (17.0% · 1.7B W): Allocated to protocol users, active community members, and cross-chain ecosystem participants through historical usage airdrops.
- Guardian Nodes (5.1% · 510M W): Distributed to institutional validator entities operating Guardian infrastructure to align long-term incentives.
- Core Contributors (12.0% · 1.2B W): Allocated to founding engineers and core protocol contributors, subject to multi-year vesting lockups.
- Ecosystem and Incubation (31.0% · 3.1B W): Reserved for developer grants, strategic partner integration programs, and future liquidity expansion.
- Strategic Network Financing (11.6% · 1.16B W): Distributed to early institutional backers who supported protocol development.
- Foundation Treasury (23.3% · 2.33B W): Dedicated to ongoing research, formal verification audits, and legal/regulatory operations.
2. MultiGov: The First Multichain Native Governance Engine
Historically, governance tokens deployed across multiple chains suffered from fragmented voting power. DAOs were forced to require users to bridge their tokens back to a single canonical chain (usually Ethereum L1) to cast votes, incurring massive gas fees and disenfranchising smaller holders.
Wormhole engineered MultiGov in collaboration with Tally. MultiGov allows W token holders on Ethereum, Solana, Arbitrum, Optimism, and Base to cast governance votes natively on their chain of choice without paying bridging fees. MultiGov collects signed vote receipts across chains using Wormhole Queries and VAAs, aggregating voting weight atomically on-chain. This represents a monumental leap forward in decentralized autonomous organization architecture.
Historic Security Exploits, Architectural Hardening, and Risk Analysis
A rigorous architectural assessment must analyze the protocol's historical failure modes and the comprehensive engineering remediations that followed.
1. The February 2022 Solana Bridge Exploit ($326 Million)
On February 2, 2022, Wormhole suffered one of the largest security exploits in decentralized finance history, resulting in the theft of 120,000 Wrapped ETH (wETH) valued at approximately $326 million. Jump Crypto subsequently backstopped the protocol by depositing 120,000 ETH to fully restore user funds.
The root cause was not a cryptographic failure of the Guardian Network or ECDSA multi-signatures, but an implementation vulnerability within the Wormhole Solana smart contract:
- Instruction Sysvar Spoofing: On Solana, verifying Secp256k1 signatures typically relies on the native
instructions_sysvar, which tracks previous program calls within the same transaction. The Wormhole contract utilized a helper function calledload_current_indexto verify that a signature check had occurred. - The Deprecated Function Flaw: Solana had recently deprecated
load_current_indexin favor ofload_instruction_at_checked. The deprecated function failed to strictly verify that the address of the supplied instruction sysvar matched the authentic Solana system sysvar program ID. - The Exploit Vector: The attacker created a fraudulent account, populated it with spoofed instruction data claiming that 19 valid Guardian signatures had been executed, and passed this fake account into the unpatched Wormhole contract. The contract accepted the spoofed account, validated a forged VAA, and allowed the attacker to mint 120,000 wETH without locking any collateral on Ethereum.
2. Architectural Hardening: The Global Accountant and Governor Module
In response to the exploit, the Wormhole engineering team completely overhauled the protocol's defensive architecture, establishing a defense-in-depth model that guarantees security even if an individual smart contract exhibits a software bug:
- The Global Accountant: An on-chain accounting state machine deployed directly into Guardian daemon logic. The Global Accountant tracks the absolute balance of locked assets across all origin chains. If a VAA attempts to release or mint more tokens on a destination chain than are verified as physically locked in the origin vault, the Guardians automatically refuse to sign the VAA, rendering contract-level mint exploits mathematically impotent.
- The Governor Module: A real-time rate-limiting daemon operating inside every Guardian node. The Governor monitors the aggregate USD value of cross-chain flow exiting any connected blockchain. If aggregate volume exceeds a configured threshold (e.g. $10 million in 24 hours), the Governor automatically buffers and delays remaining transactions for manual review, preventing instantaneous drainage of bridge reserves.
- Continuous Open-Source Audits and Bug Bounties: Wormhole established the industry's largest bug bounty program: offering up to $10 million for critical vulnerability discoveries: alongside continuous formal verification of all Core Contract bytecodes.
3. Critical Trade-offs: The 19-Guardian Multi-Sig vs. ZK and Optimistic Bridges
Despite its proven track record and defense-in-depth architecture, Wormhole embodies an explicit cryptoeconomic trade-off: proof-of-authority multi-signature security.
- Trust Assumptions: Security relies on the integrity, operational independence, and private key security of 19 institutional entities. Unlike Proof-of-Stake protocols where validators have bonded tokens that are automatically slashed via smart contracts upon misbehavior, Guardians do not bond slashable collateral. Their security alignment is driven by corporate reputation, legal standing, and operational alignment.
- Comparison to Zero-Knowledge (ZK) Bridges: Emerging ZK interoperability protocols (such as Succinct or Polymer) rely on mathematical zero-knowledge proofs to verify consensus state headers directly inside target chain virtual machines. ZK bridges achieve absolute trust-minimization (relying only on source chain math rather than off-chain validator committees), but incur significantly higher on-chain verification gas costs and higher latency for proof generation.
- Liveness and Censorship Vectors: If 7 of the 19 Guardians experience simultaneous infrastructure failure, network partitioning, or coordinated regulatory pressure, the entire Wormhole protocol halts globally. Wormhole trades pure cryptographic trustlessness for universal multi-chain compatibility, sub-second latency, and horizontal scalability.
Conclusion
Wormhole has evolved from a targeted token bridge into one of the most sophisticated, resilient, and widely utilized generalized cross-chain messaging substrates in Web3. By cleanly separating on-chain emission from off-chain attestation and execution, the protocol achieves seamless interoperability across radically distinct virtual machines: from EVM and SVM to Move and CosmWasm.
Through its 19-node Guardian Network, standardized Verified Action Approval (VAA) format, and decentralized relayer topologies, Wormhole processes billions of dollars in cross-chain value with deterministic finality. Innovations such as Native Token Transfers (NTT), Wormhole Gateway, and Wormhole Queries address historical pain points in liquidity fragmentation and cross-chain state reading, while post-exploit security primitives like the Global Accountant and Governor Module provide institutional-grade protection against systemic threats.
While the 19-guardian multi-signature architecture involves clear trade-offs against purely trustless zero-knowledge systems, Wormhole's battle-tested execution environment, MultiGov multichain governance, and aggressive engineering standards firmly position it as an indispensable routing backbone for the multi-chain decentralized economy.